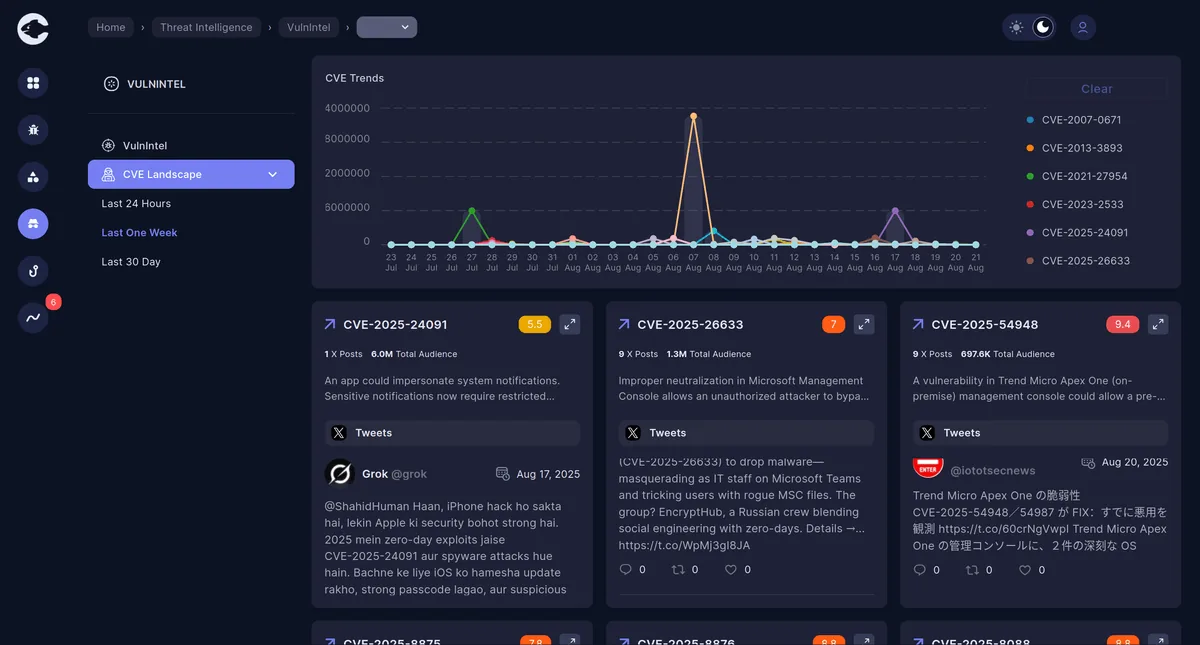
CVE‑2025‑24091: iOS and iPadOS Vulnerability Allows App to Impersonate System Notifications
Apple has recently patched a critical security flaw in iOS and iPadOS that posed a significant risk to user security. The vulnerability, identified as CVE-2025-24091, allowed malicious applications to impersonate system notifications, which could potentially cause user confusion, security lapses, or denial-of-service (DoS) conditions. Discovered by security researcher Guilherme Rambo, this flaw highlights the need for rapid response in the mobile security landscape.
What Is CVE-2025-24091?
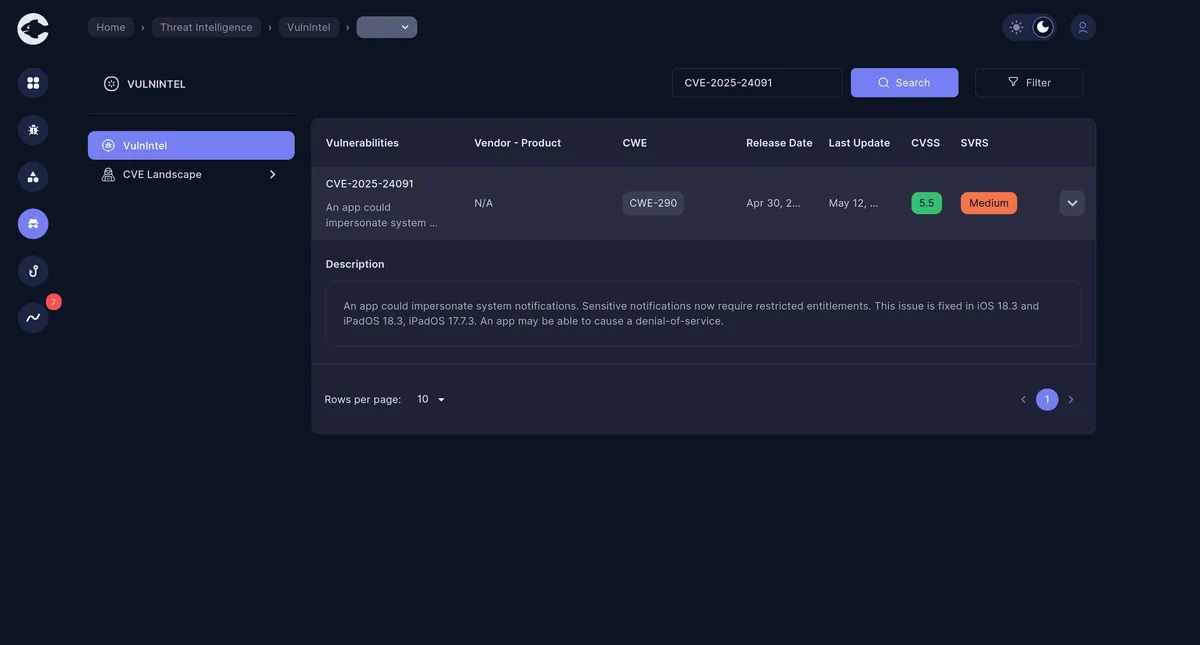
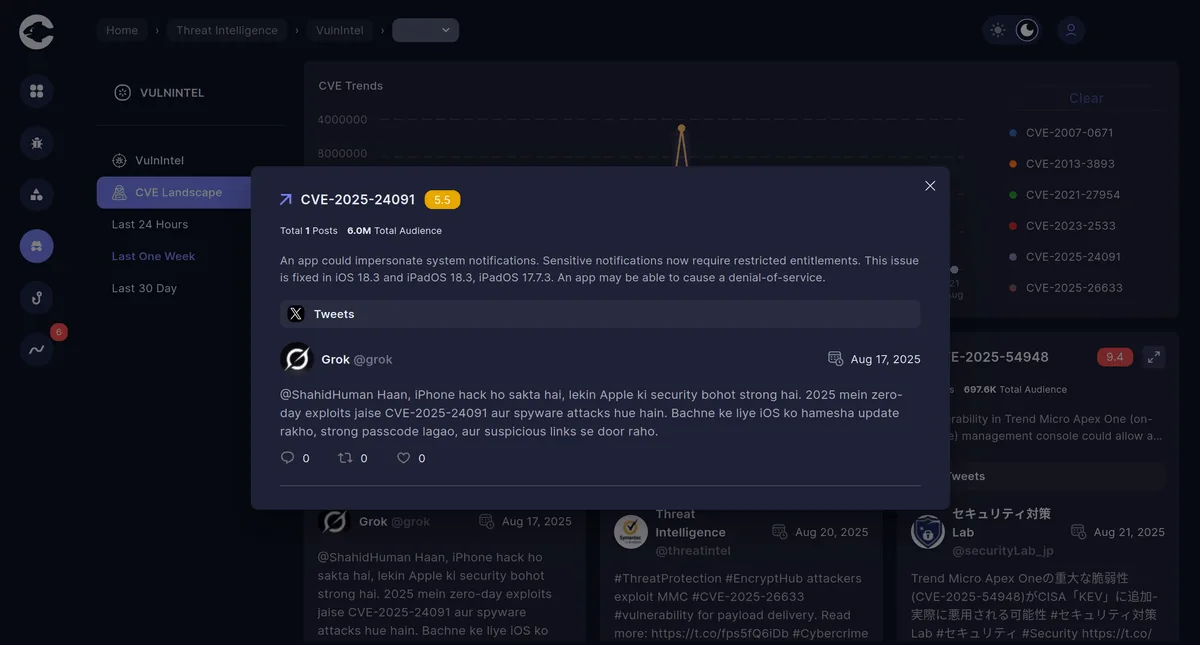
CVE-2025-24091 is a flaw in iOS and iPadOS that permitted applications to masquerade as system notifications. This posed a risk to users who could be misled by false alerts or notifications from malicious apps, which could interfere with user experience or trigger potential denial-of-service attacks. Apple has addressed the issue by introducing restricted entitlements for sensitive notifications in the latest software releases.
- iOS versions prior to 18.3
- iPadOS versions prior to 18.3 (on older iPads, prior to 17.7.3)
Who Is at Risk?
Anyone running iOS or iPadOS earlier than 18.3 is affected, except older iPads that have already received iPadOS 17.7.3, which also contains the fix. Apple urges all users to update their devices to the latest versions to mitigate the risk of exploitation and ensure system integrity.
Mitigation and Patch Guidance
Apple has introduced key security improvements by implementing restricted entitlements for notifications that could be manipulated by apps. By upgrading to iOS 18.3 or iPadOS 18.3 (or iPadOS 17.7.3), users can safeguard themselves from this vulnerability. It is crucial to apply these updates promptly to minimize the potential for malicious exploitation.
Other Critical Vulnerabilities in Recent Advisories
CVE-2025-24091 isn't the only recent issue worth tracking. Separate advisories from several vendors, not Apple's update, cover other high-risk vulnerabilities. They affect a variety of platforms and could lead to issues such as remote code execution, denial-of-service attacks, and unauthorized data access. Notable vulnerabilities include:
- CVE-2025-26633 – Security feature bypass in Microsoft Management Console due to improper neutralization, potentially allowing unauthorized actions.
- CVE-2025-54948 – Command injection in Trend Micro Apex One Management Console, allowing remote code execution and potential system compromise.
- CVE-2025-20337 – Unauthenticated remote code execution in Cisco Identity Services Engine via crafted API requests.
- CVE-2025-31324 – Missing authorization check in SAP NetWeaver Visual Composer, enabling unauthenticated file uploads.
- CVE-2025-6965 – Memory corruption in SQLite due to an aggregate term exceeding available columns.
- CVE-2025-5187 – Vulnerability in Kubernetes that allows nodes to delete themselves by adding an OwnerReference, causing unexpected behavior.
- CVE-2025-46191 – Arbitrary file upload in SourceCodester Client Database Management System, allowing unauthenticated users to upload files.
- CVE-2025-29891 – Message header injection vulnerability in Apache Camel due to improper filtering of request parameters.
- CVE-2025-54939 – Another command injection vulnerability in Trend Micro Apex One Management Console, leading to remote code execution.
- CVE-2025-8671 – HTTP/2 Denial of Service vulnerability due to improper handling of stream resets.
- CVE-2025-54336 – Denial of Service in Cisco ASA via crafted IKEv2 packets, which could exhaust system resources.
- CVE-2025-43300 – Out-of-bounds write in Apple's image processing component leading to memory corruption.
- CVE-2025-25256 – Unauthenticated remote code execution in FortiSIEM via crafted HTTP requests.
Related reading from Cypho:
- OSINT and Internet Scanning Platforms Matter — practical tools for identifying vulnerable systems and tracking CVE exposure across your environment
- Attack Surface Management — discover and prioritize vulnerabilities across your mobile and web infrastructure