Neptune Loader: Exposing the Hidden Realms of Malware Command And Control / Vulnerability that exposes affected machines
Introduction
This post talks about a vulnerability that we discovered in Neptune loader. Neptune loader is used for remotely controlling your device, it has some features that help attackers to easily use it. This vulnerability allows us to get information about the affected machines that are called bots. Neptune has a web interface that is used for control. We found a serious vulnerability. The post shares details that can help cybersecurity experts find and fix this weakness.
What is Neptune?
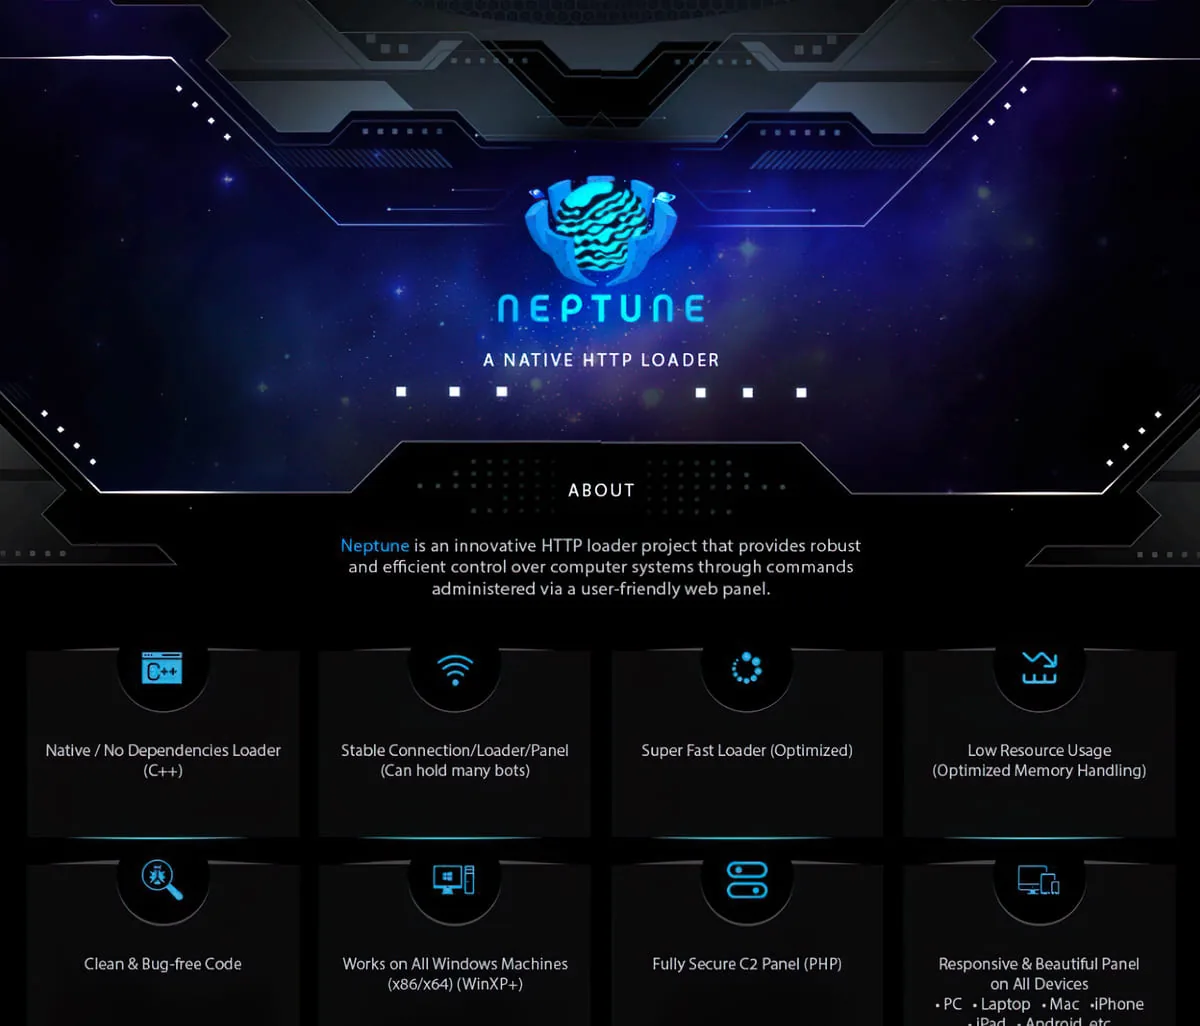
In the threat actor's exact words : "Neptune is an innovative HTTP loader project that provides robust and efficient control over computer systems through commands administered via user-friendly web panel." First seen date is 2023 November 22, user named "M0HX" shared a post on hackerforums.net and promoted a loader named Neptune.
During our examination of Neptune loaders, we found something interesting. One of them has a backup file for a database (SQL).
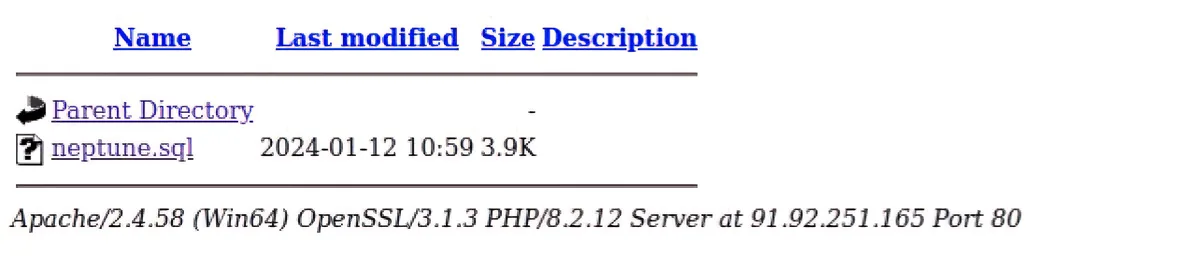
This file has default usernames and passwords. This discovery gives us important clues about how the loader is set up and might help us understand its security better. As we look into this more, we can learn more about possible issues and weaknesses related to this Neptune loader.

The passwords were stored as bcrypt hashes. bcrypt is a deliberately slow password-hashing scheme, not encryption, so there is nothing to decrypt: the only way in is to guess candidate passwords and hash each one until one matches. Our team did exactly that and recovered the password.
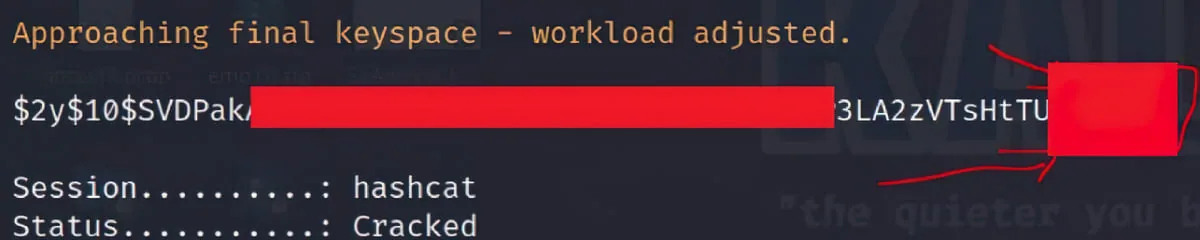
Upon successfully gaining access to the loaders' dashboard, we conducted a thorough analysis of the application. The objective was to examine every aspect of the system, actively seeking out any potential vulnerabilities that could be exploited. After some time we discovered how our application collects information from the database.
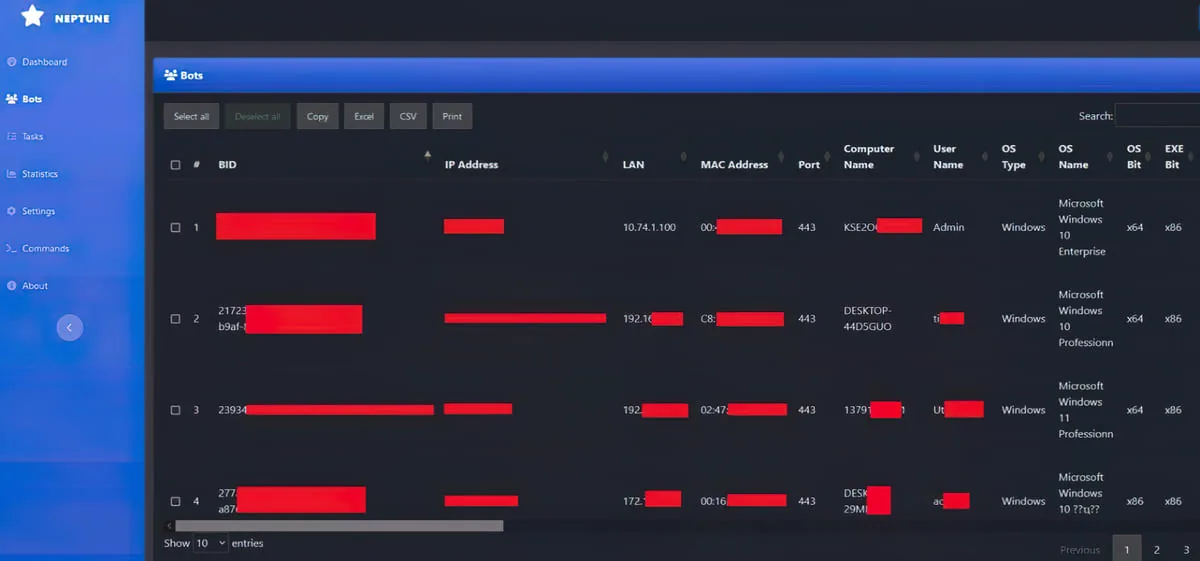
We discovered an important security vulnerability within the application, a Broken Access Control (Improper Session Management) issue. This vulnerability exposes a flaw in how the system manages user sessions, enabling unauthorized access to information related to affected machines(Bots). By exploiting this weakness, an unauthorized user gains visibility into sensitive data that should otherwise be restricted.
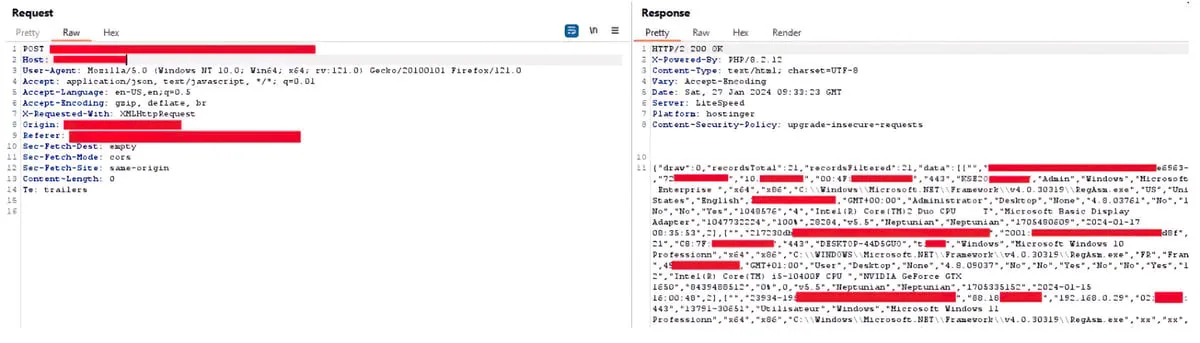
The application uses AJAX requests to render a datatable containing the victim's data. A notable vulnerability was identified in the lack of session validation for the endpoint utilized in AJAX requests. This oversight meant that the application did not properly verify the session information, potentially exposing sensitive victim data to unauthorized access or manipulation.
Protecting Against Neptune Loader
Proactive Threat Mitigation: Use proactive measures by utilizing Indicators of Compromise (IoCs) to actively search for potential Neptune Loader infections within your IT environment. This strategic approach involves actively hunting for signs of compromise, allowing for timely detection and mitigation of potential security threats.
Comprehensive Cybersecurity Education: Implement a cybersecurity awareness training program designed to empower employees with the knowledge and skills to recognize and respond effectively to cyberattacks. This educational initiative aims to enhance the overall cybersecurity resilience of the workforce, fostering a proactive and vigilant approach in safeguarding against potential threats posed by malware attacks.
Leverage Advanced Threat Intelligence: Utilize the CYPHO platform, an advanced threat intelligence tool, to enhance your cybersecurity defenses. This platform offers valuable insights and real-time information about emerging threats, enabling your organization to stay ahead of potential risks and bolster its overall security posture.
IOCs
| Type | Indicator |
|---|---|
| IP Address | 94.156.65.54 |
| Domain | mfuk.app |
| Domain | 54.lan-za2-1.static.rozabg.com |
| Domain | tdboat.online |
| IP Address | 91.92.240.161 |
| SHA-256 | 2a3549512f5f9cf1b11a26897a79532adc548c3000fb7b07fcae6b49cd5222ad |
A second SHA-256 in the original version of this post was published incomplete (63 of 64 characters) and has been removed until it can be verified against the sample.
Related reading from Cypho:
- Codefinger Ransomware: The Operation Targeting Critical Infrastructure Worldwide — another emerging threat leveraging advanced evasion and double extortion
- Threat Intelligence Platform — operationalize IOCs and track malware infrastructure with Cypho's threat intelligence capabilities